L.E.A.D. IT launches School IT on a Page app
At L.E.A.D. IT Services we don't just support schools against these standards; as part of LEAD Academy Trust, we work to them ourselves. We know what it's like to sit in front of a board of trustees and be asked how you know your filtering works or your backups would restore. This guide sets out what the DfE actually expects, in plain English, alongside the practical detail we use every day with the schools and trusts we partner with.
Chris Edwards, LEAD IT Services
The DfE’s digital and technology standards describe what safe, reliable and well-governed technology looks like in schools and colleges. The full framework covers many areas, including network cabling, servers and storage, cloud solutions, laptops, desktops and tablets, and IT support. Six of these have been designated core standards. These are the foundations everything else depends on, and they are the ones schools are expected to meet by 2030.
The standards were first published in 2022 and have been updated several times since. In 2025, following a national consultation on narrowing the digital divide, the DfE confirmed its 2030 ambition for the six core standards. The most recent update, in September 2026, strengthened several cyber security requirements, including faster patching and immutable backups.
The standards are not legislation in their own right. However, calling them ‘optional’ would be misleading, for four reasons:
In practice, a school or trust that cannot evidence progress against the six core standards will struggle to satisfy governors, trustees, auditors and insurers.
|
Core standard |
What it requires, in short | When the DfE expects it |
Key evidence to hold |
|---|---|---|---|
| Broadband internet | Full fibre; minimum 100Mbps down / 30Mbps up (primary) or 1Gbps down and up (secondary, all-through, FE); backup connection with automatic failover; firewall and filtering | Full fibre at contract renewal or when available; backup alongside a new connection; security now | Contract, speed tests, failover test, firewall configuration |
| Wireless network | Wi-Fi 7 when upgrading; full coverage based on heat mapping; central management; strong security (WPA3, segregation, MFA for admins) | When the current solution is underperforming or unsupported | Survey or heat map, access point inventory, support dates |
| Network switching | 1Gbps to the desktop; multi-gigabit for access points and servers; 2×10Gbps uplinks; 5-year support; central management; network access control; resilient core on UPS | When replacing underperforming or unsupported kit | Switch inventory, firmware and support status, network diagram |
| Digital leadership and governance | SLT digital lead; contracts, asset and information asset registers; digital technology in DR/BC plans; strategy covering at least 2 years, reviewed annually | Registers now; strategy before the next budget cycle | Named lead, registers, tested DR plan, approved strategy |
| Filtering and monitoring | Named SLT member and governor; annual review; IWF and CTIRU blocklists; separate staff and student profiles; weekly monitoring reports | Now | Review record, check log, role assignments, incident records |
| Cyber security | Annual risk assessment reviewed termly; awareness training; firewall and anti-malware; MFA; licensing and 14-day patching; 3 immutable backup copies tested termly; incident reporting | Now, or as soon as possible | Risk register, training records, patch reports, backup test logs |
Almost everything a modern school does depends on its internet connection, including cloud MIS, online assessment, Microsoft 365 or Google Workspace, VoIP telephony and safeguarding systems. The broadband standard has three parts.
Use a full fibre connection. Broadband should be delivered over full fibre, such as a leased line or fibre to the premises (FTTP). Copper-based services do not meet the standard, and this includes FTTC (“fibre to the cabinet”), which runs over copper for the final stretch. The minimum speeds are:
The DfE expects schools to move to full fibre at the end of their current contract, or as soon as full fibre becomes available. Any new contract on a non-fibre service should allow an upgrade as soon as fibre arrives.
Have a backup connection. Broadband is now an essential service, so a single line is a single point of failure. The standard calls for a combination of:
Have appropriate security and safeguarding systems. A correctly configured firewall, either on premises or managed by your provider, plus content filtering that meets KCSIE.
What we see in schools: Primaries still on FTTC are common. So are backup lines that have never been tested, and backup connections that bypass the school’s filtering altogether. The filtering standard explicitly requires all internet feeds to be filtered, including backup connections and portable Wi-Fi devices.
Evidence to hold: connection type and contract end date, speed tests taken during the school day, a record of the last failover test, and firewall ownership and configuration.
As learning moves onto laptops, tablets and cloud platforms, Wi-Fi has to work wherever teaching happens, including halls, sports areas and outdoor spaces where needed.
Use the latest wireless standard when you upgrade. When an upgrade is due, the DfE now specifies Wi-Fi 7 (802.11be) as the minimum. The network should support segregation and quality of service (QoS), and the network interface speeds of the access points (typically 1, 2.5, 5 or 10Gbps) need to match the switching behind them.
Provide full coverage. Coverage should reflect how many people use each space, not just floor area. That can mean an access point in every classroom and higher-capacity units in halls. The design should be based on a wireless heat-mapping survey.
Manage the network centrally. A central platform should configure the access points, monitor performance, raise alerts and push security updates automatically. The DfE also expects manufacturer warranty and support, administrator training, and a configuration file that can restore the school’s original setup.
Stop unauthorised access. Measures include VLANs, access control lists, segregated guest access, WPA3 authentication, wireless intrusion protection, certificate-based authentication, and MFA for privileged and technical accounts.
When: The DfE expects this standard to be met when an existing solution is underperforming or out of support. That makes it a planning and budgeting issue, which a refresh schedule should address.
What we see in schools: Access points that are well past end of support, consumer-grade kit in mobile classrooms, and guest and pupil devices sharing a network with staff systems.
Evidence to hold: a coverage survey, an access point inventory with support end dates, the management platform in use, and a network segregation design.
Switches connect devices, access points, servers and the internet. They are also where many schools lose performance without realising it: a Wi-Fi 7 access point behind an old 100Mbps switch will never deliver what it promises.
Fast, reliable and secure connections. The requirements are:
Power over Ethernet (PoE) must meet the power requirements of the devices it feeds, such as access points, CCTV, door access control and phones.
Central management and support. A central management tool should cover both core and edge switches. Each switch needs a minimum of five years of manufacturer warranty and support, including firmware updates. Equipment that can no longer receive security updates should be replaced.
Security features. These include network access control (NAC), segregation and QoS, secure and documented administrator accounts, and automatic firmware updates backed by manual checks.
Resilience. Critical core switches should have two power supplies, two management modules and dual connections to other critical infrastructure, and should be connected to at least one UPS.
What we see in schools: Unmanaged desktop switches in classrooms, core switches with no UPS, and no current network diagram, which the cyber security standard also requires.
Evidence to hold: a switch inventory with firmware versions and support end dates, a current network diagram, and UPS and redundancy arrangements.
This is the standard that makes the other five achievable, and it is often the one with the largest gap. The DfE sets out four requirements and advises completing the first three before the fourth.
Assign a senior leader responsible for digital technology. The headteacher appoints an SLT digital lead. This is usually someone with teaching experience rather than a technical specialist. They are accountable for the digital strategy, for reviewing how well IT support is performing, and for staff and pupil training needs. Governors and trustees should consider appointing a digital link governor or trustee.
Keep registers up to date. Three registers are needed:
The DfE provides templates for all three through its Plan technology for your school service.
Include digital technology in disaster recovery and business continuity plans. These plans should define what a “disaster” means for your school. They should name the recovery team and key contacts, be tested at least once a year, and be kept in both printed and secure cloud form, so they remain available during a cyber incident.
Have a digital technology strategy reviewed every year. The strategy should cover at least two years, align with the school development plan, cover refresh and replacement, and be reviewed at least annually. It is overseen and challenged by governors or trustees.
What we see in schools: Registers held in spreadsheets that nobody owns, strategies with no costed plan behind them, and continuity plans that were written once and never tested.
Evidence to hold: the name of the digital lead, current versions of all three registers, a DR/BC plan with its last test date, and an approved strategy with evidence of its annual review.
Filtering and monitoring are safeguarding responsibilities first and technology responsibilities second. The DfE says schools should already be meeting this standard. It has four parts.
Assign roles and responsibilities. Governing bodies should name a member of SLT and a governor responsible for the standard. The DSL leads on safeguarding and online safety, including checking reports and giving governors assurance. IT support maintains the systems and produces reports.
Review provision at least once every academic year. SLT, the DSL, IT support and the responsible governor should carry out the review together. It should consider:
Checks should be logged, recording when they happened, who carried them out, what was tested and what action followed. A further review should take place whenever new technology, AI tools or significant changes are introduced.
Block harmful content without unreasonably affecting teaching. The filtering provider must be an IWF member, signed up to the CTIRU list, and those blocklists must be impossible for anyone to disable. Filtering should:
The September 2026 update also expects schools to consider how their filtering handles AI-generated and dynamic content.
Monitor effectively. Staff should supervise pupils in person whenever devices are in use. Where technical monitoring is used, the minimum is weekly reports, with immediate alerts for high-risk incidents. Every incident needs a documented record of the action taken and the outcome.
What we see in schools: Annual reviews that happened but were never written down, blanket filtering profiles, and backup connections or mobile hotspots that bypass the filter.
Evidence to hold: the review record, a log of checks, the names of the responsible SLT member and governor, and incident and response records.
Cyber attacks can close schools, compromise safeguarding data and cost huge sums to recover from. This is the most detailed of the six standards and has the most recent updates. It covers seven areas.
Conduct a cyber risk assessment every year and review it every term. The SLT digital lead coordinates this with IT support, the DPO, the estates team, the finance team and governors. Cyber risks belong in the risk register, and a cyber response plan should form part of the business continuity plan. That plan is also a condition of RPA cover.
Create a cyber awareness plan. This means an acceptable use policy that everyone signs, including guests and supply staff. It also means cyber training at least once a year for staff, pupils and at least one governor or trustee. For RPA members, evidence of the free NCSC training is required annually.
Secure technology with a firewall and anti-malware. The firewall should be correctly configured, with termly firmware checks, MFA on the admin interface and a documented, termly-reviewed record of any inbound rules. Anti-malware should be centrally managed. USB storage should be blocked by default. Email should be configured to prevent spoofing.
Control user accounts and access. Every user needs unique credentials, and each account should have only the access its role requires. MFA is required for all staff accounts that access cloud services or remote systems, and for all IT admin accounts. There should be a joiners, movers and leavers process, with accounts reviewed each term. Separate admin accounts should never be used for day-to-day work.
License technology and keep it up to date. All software must be licensed and supported. Under the September 2026 update, critical and high-risk vulnerabilities (CVSS 7.0 or above) must be patched within 14 days. Devices that cannot be patched should be isolated.
Back up data and review the plan every year. Keep at least three copies of important data on two separate devices, with one copy off site. Backups should be immutable, meaning they cannot be altered once written. Restores should be tested and logged every term.
Report cyber attacks. Incidents should be reported to your RPA or insurer, Report Fraud and the DfE sector cyber team. Depending on the incident, you may also need to report to the NCSC, and to the ICO within 72 hours if a high-risk data breach may have occurred.
How this relates to Cyber Essentials: The DfE standards focus on governance, process and strategy. Cyber Essentials is an annual, independently assessed certification of technical controls. Colleges must hold it. For schools it is optional, but it is a strong, externally verified way to demonstrate the technical side of this standard.
What we see in schools: MFA switched on for some staff but not all, backups that have never been restored in a test, patching that takes weeks rather than days, and governors who have never received cyber training.
Evidence to hold: the risk assessment and termly reviews, training records, MFA coverage reports, patch compliance reports, backup and restore test logs, penetration test results, and an incident register.
The standards are closely linked, and treating them separately is one of the most common and costly planning mistakes:
| Role | Main responsibilities |
|---|---|
| Governors or trustees | Strategic oversight and challenge; named filtering and monitoring governor; digital link governor or trustee; cyber training for at least one member |
| Headteacher or CEO | Appoints the SLT digital lead; approves strategy and incident reports |
| SLT digital lead | Owns the strategy, registers, DR/BC planning and cyber risk assessment; coordinates everyone else |
| DSL | Leads on filtering and monitoring reports and responses; advises on the safeguarding impact of technology decisions |
| DPO | Owns the information asset register; carries out DPIAs; advises on breaches |
| School business leader or CFO | Contracts register, budgets and procurement |
| IT support (in-house or outsourced) | Delivers and evidences the technical requirements; reports on progress |
The date “2030” can create a false sense of time. Much of the filtering and monitoring and cyber security standards should already be in place. The infrastructure standards are triggered by refresh and contract cycles, so most schools will have only one opportunity to get each of them right before 2030.
For trusts, the challenge is consistency and visibility across multiple schools. Good practice includes:
Some responsibilities usually sit centrally, such as strategy, procurement and cyber governance. Others must remain at school level, such as the DSL’s day-to-day filtering and monitoring role.
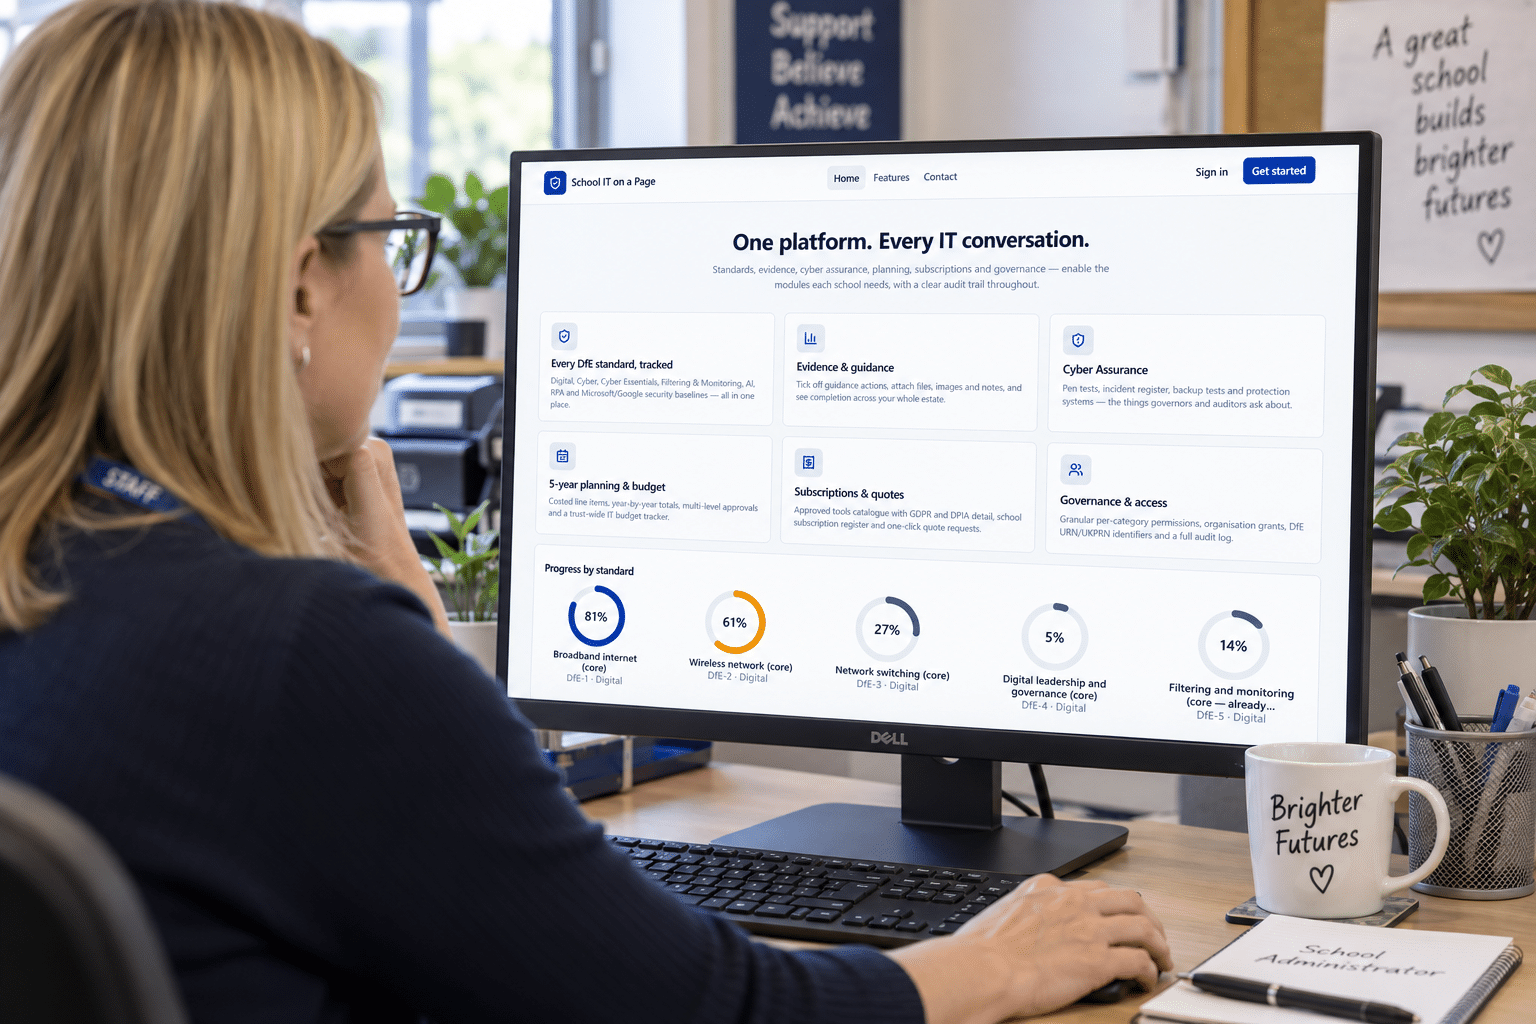
School IT on a Page was designed and built by L.E.A.D. IT Services to do exactly this job. It:
One-click reports give governors, trustees and auditors a current picture in seconds.
As part of LEAD Academy Trust, we understand the standards from the inside. We offer fully managed IT support, infrastructure design, cyber security, safeguarding and filtering, and strategic consultancy for schools and trusts. Talk to our education team about a baseline review against the six core standards.
Not in themselves. However, the Academy Trust Handbook expects trusts to be working towards them by 2030, and the filtering, monitoring and cyber elements support statutory safeguarding duties under KCSIE. Several cyber requirements are also conditions of RPA cover.
Yes. The 2030 ambition applies to all schools and colleges in England. The Academy Trust Handbook reference applies specifically to trusts.
The DfE says schools should already be meeting the filtering and monitoring standard, and most of the cyber security standard, including risk assessment, access control, licensing, backups and incident reporting. The broadband, wireless and switching requirements are generally triggered by contract renewals and equipment refreshes.
Primary schools need at least 100Mbps download and 30Mbps upload. Secondary schools, all-through schools and FE colleges need a connection capable of 1Gbps download and upload, delivered over full fibre, with a backup connection of a different type.
When you upgrade, the DfE specifies Wi-Fi 7 (802.11be), centrally managed, with coverage designed using a heat-mapping survey.
The DfE standards cover cyber governance, process and strategy for schools. Cyber Essentials is an annual, government-backed certification of technical controls. Colleges must hold it; for schools it is optional but good evidence.
At least once every academic year, and additionally whenever new technology, generative AI tools or significant changes are introduced. Keep a written record of each review and a log of checks.
A member of the senior leadership team appointed by the headteacher, usually with teaching experience. They don’t need to be a technical expert, but they are accountable for the strategy and for making sure the standards are met.
Keep evidence against each standard in one place, with a clear audit trail and a costed plan for closing gaps. Platforms such as School IT on a Page are built for this purpose.